We prepare before the fight
Proactive threat modeling, hardening, and risk assessment, before an incident forces your hand.
Our Mission
Proactive Risk exists for one reason: to protect those who rely on technology before failure becomes damage. We do not wait for incidents. We do not accept avoidable risk. We operate forward—with discipline, integrity, and purpose.
The company
Founded in 2001 by Tom Brennan, Proactive Risk is an SDVOSB-certified cybersecurity firm headquartered in Denville, New Jersey, serving clients nationwide. The firm provides fractional CISO leadership, 24/7 managed detection and response, CATSCAN® adversarial penetration testing, third-party risk management, and compliance services for businesses and government agencies. Proactive Risk is a member of the International Association of Chiefs of Police (IACP).
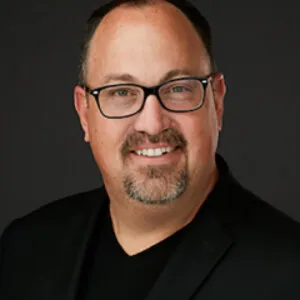
Founder & principal consultant
Founder & Principal Consultant — United States Marine Corps Veteran · Practicing CyberAdvisor℠
Tom is not just the founder — he is a practicing principal consultant who leads engagements directly. Every client relationship starts with Tom's hands-on assessment of risk posture, business context, and operational gaps.
Cybersecurity executive. ISC2 Certified Information Systems Security Professional (CISSP); National Security Agency IAM; Former OWASP Foundation Board Member; Former U.S. Regulatory Affairs, CREST International; Past Technical Director, SAFECode; Co-Founder, NonprofitCyber.org; Author on cybersecurity and risk governance; Advisor to NYU, NJIT, CCM, and HPU. Tom brings 20+ years of adversarial operations, governance, and risk leadership to every engagement.
We've Got Your Six
Preparation, direct advice, and steady execution shape how Proactive Risk works with the people responsible for the outcome.
Proactive threat modeling, hardening, and risk assessment, before an incident forces your hand.
Continuous monitoring, honest reporting, and direct advice, even when it's not what you want to hear.
When an incident hits, we do not panic. We contain, remediate, and restore with precision.
Operating principles
These principles keep the work plainspoken, accountable, and focused on the responsibility we take on.
We tell the truth about risk. We do the right thing when it's easy, and especially when it's not.
We speak plainly. We challenge assumptions. We confront problems early, before they become crises.
We do not quit on the mission, the client, or each other. When we take responsibility, we own it fully.
Memberships & affiliations
Proactive Risk is a proud 2026 member of the Morris County Chamber of Commerce, connecting our Denville-based team with the local business community we serve.
Membership is a professional and community affiliation, not a security certification or endorsement.Professional affiliation.
Published works
CREST
IEEE
ILPA
SAFECode
SAFECode
OWASP
OWASP
The next conversation